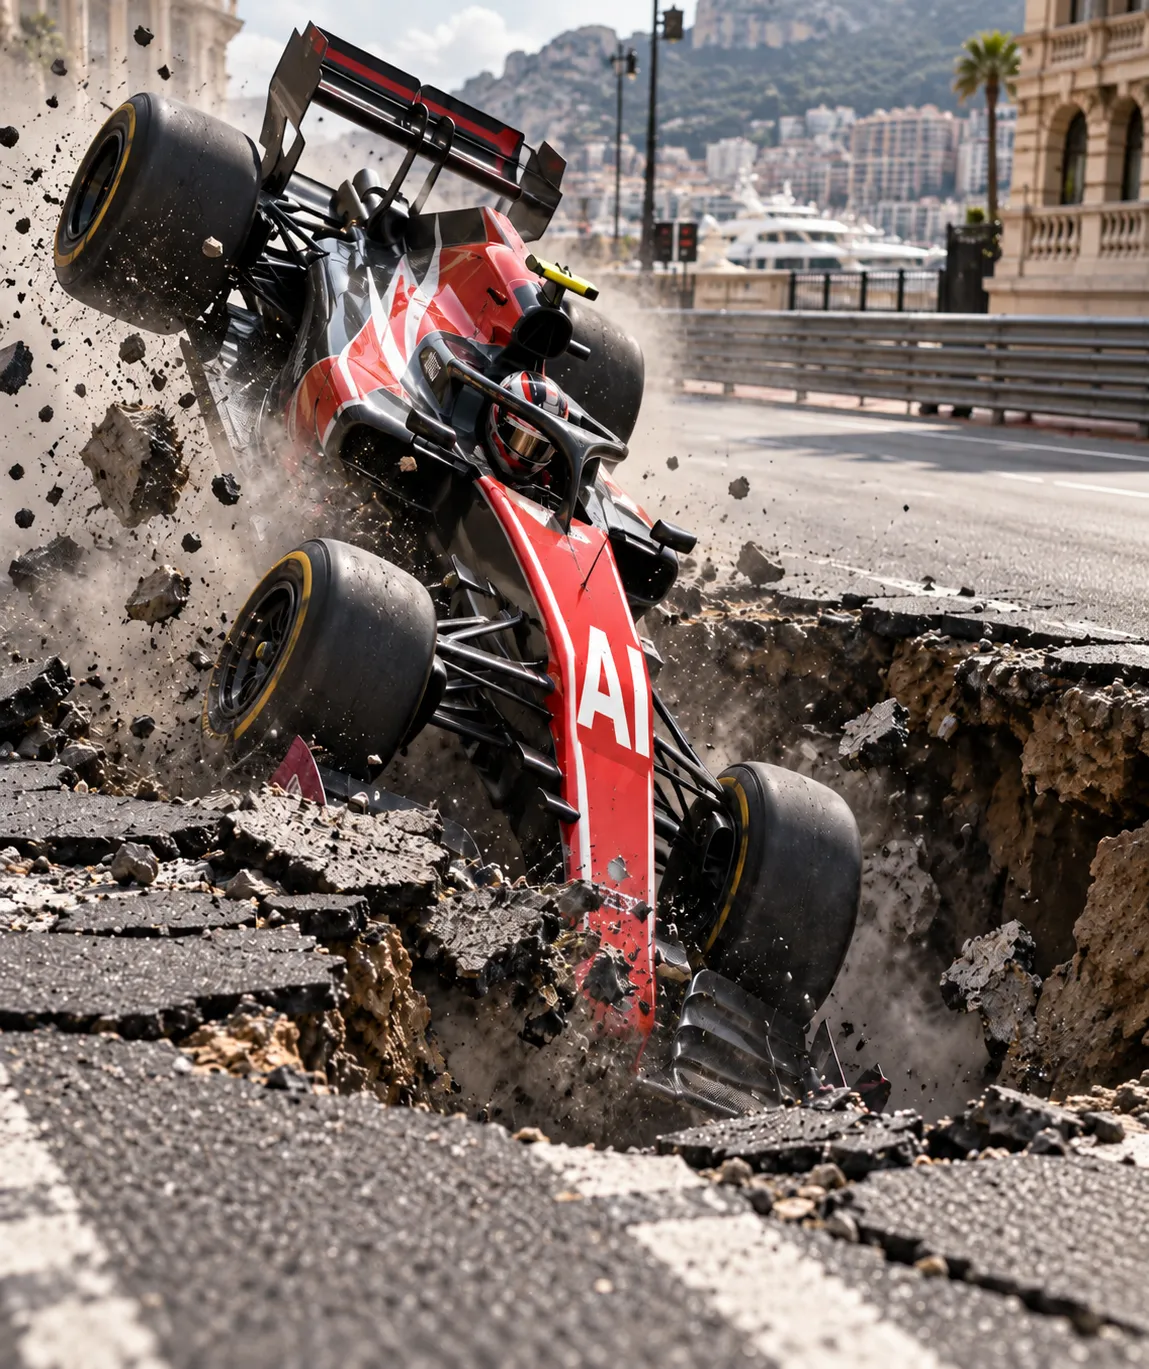
AI is like a 200mph racecar.
Don't crash it into a compliance sinkhole.
The worst words you can say are 'We are compliant' based on a self-assessment.
AI can bring you down faster than anything. Our AI Compliance Quick Start can give you the comfort you need.
Get an independent review of your cybersecurity compliance to ensure your compliance will stand up to the scrutiny of an audit.
Everyone thinks about regulations, but contracts with cybersecurity clauses and cyber insurance affirmations can hit your business harder than a regulatory fine. We look at everything and give you an honest assessment. Don't take chances.
Our job is to help you pass regulatory audits, avoid penalties, survive incident investigations, know your insurance will pay, and avoid lawsuits - so you can help the people you serve.
We’ve been advising organizations to comply since 2004, based on Mike Semel’s certifications and hands-on experience as the Chief Information Officer for a hospital. Mike has written HIPAA certification courses and a best-selling book, How to Avoid HIPAA Headaches.
Our job is to help you pass regulatory audits, avoid penalties, survive incident investigations, know your insurance will pay, and avoid lawsuits.
We’ve been advising organizations to comply since 2004, based on Mike Semel’s certifications and hands-on experience as the Chief Information Officer for a hospital. Mike has written HIPAA certification courses and a best-selling book, How to Avoid HIPAA Headaches.
THEY ARE CLOSING OUR HIPAA INVESTIGATION!
“Great news! Attached is the letter we received from the OCR saying they are closing our HIPAA case without further action. Mike, thank you so much for your assistance with the response. I can’t tell you how much we appreciate your input that greatly influenced this outcome.”
— Rebecca Stodolak
Many healthcare organizations think their HIPAA-only compliance program is enough. We Know Better.
The HIPAA Security Rule isn't your only cyber compliance challenge. HIPAA has two other rules and you must also juggle the requirements in state laws, professional licenses, contracts, and insurance policy requirements.
Unlike IT staff and Managed Service Providers, we can help with privacy and confidentiality regulations like mental health laws, STD/HIV laws, and Substance Use Disorder information laws - some of which conflict with HIPAA.
HIPAA-only strategies leave you exposed. We don’t.
We also help with state data breach laws, contracts, and cyber insurance policies—providing policy reviews, templates, checklists, and support to help compliance officers and IT directors excel.
Call Rose at
888-997-3635 x 202
We take the Risky Guesswork out of Cybersecurity and Compliance
The most common root cause of HIPAA penalties is the lack of an accurate and thorough Security Risk Analysis.
You know a good doctor wouldn't treat you by just asking questions. You want one that looks under your skin to see what is really happening.
That's why we look under your organization's 'skin' to evaluate your cybersecurity and compliance.
We Help Businesses
Comply With Everything: Federal & State Regulations, Contracts, & Cyber Insurance
Confidentially Identify Hidden Risks
Secure Your Data
Protect The People You Serve
Continue Your Operations
Protect Your Workforce Members
Protect Your Reputation
Protect Your Finances
So You Can Focus On Your Mission
We are certified to assess NIST compliance
and continuity planning.
NIST Cybersecurity Framework (CSF) 2.0
businesses, state & local government
NIST SP 800-171/CMMC Level 2
defense contractors
Mike Semel is a certified assessor for the CMMC cybersecurity program for defense contractors,
He has created a training course for the NIST CSF 2.0.
FREE BOOK!
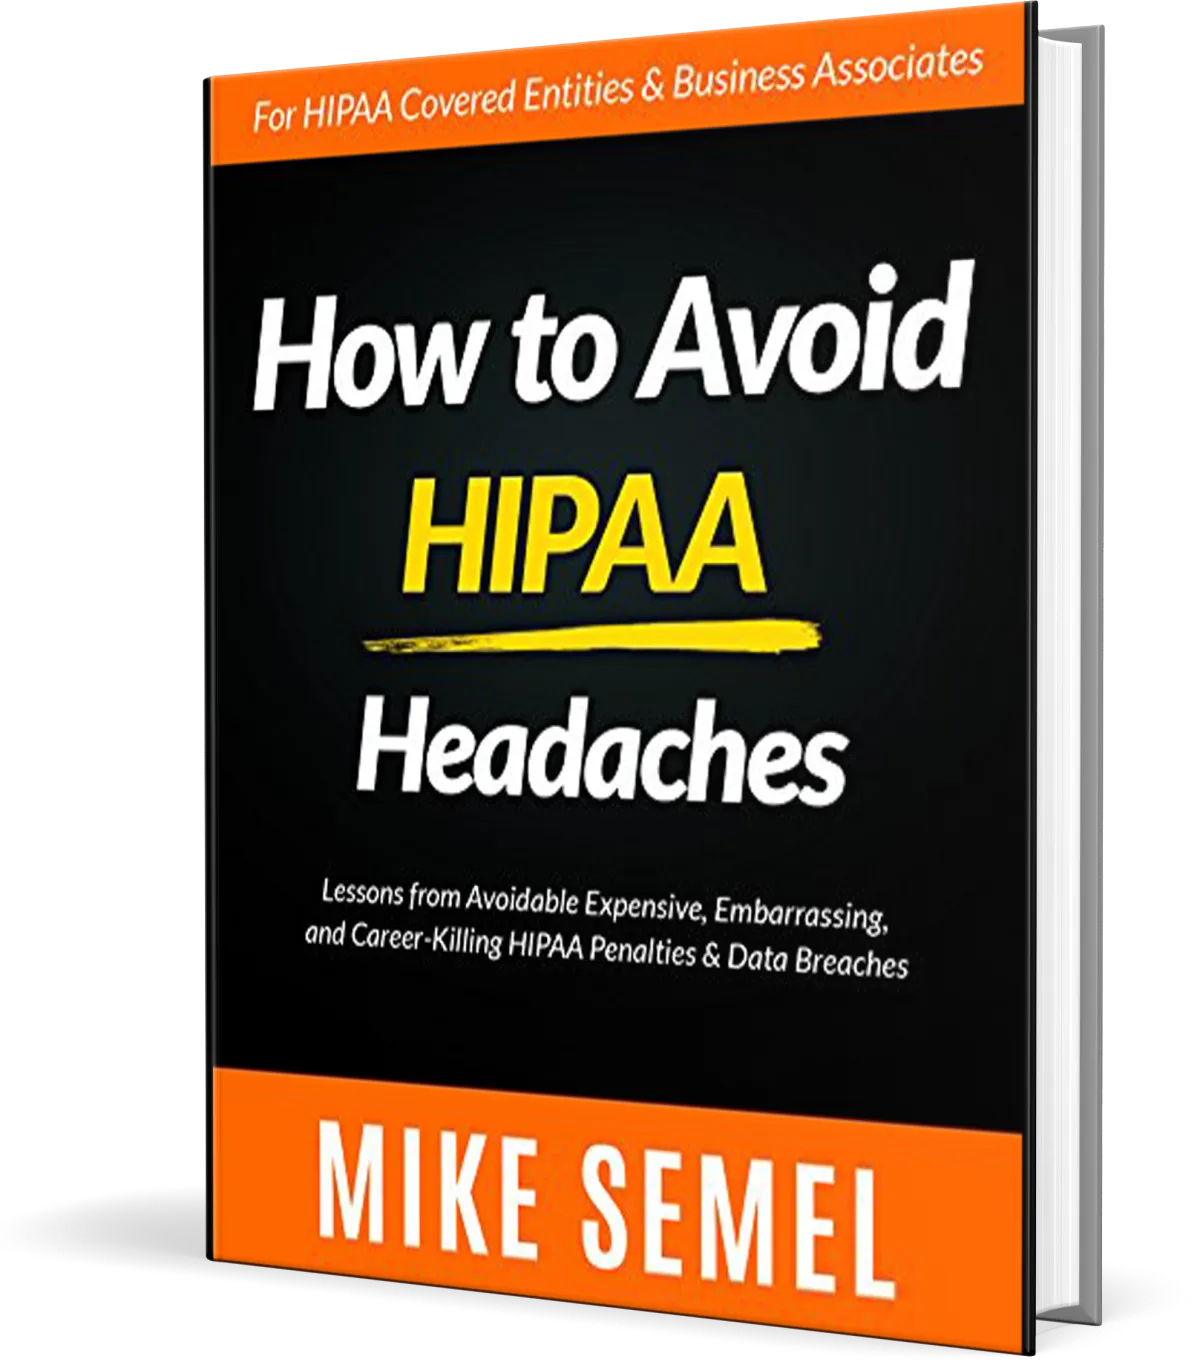
How to Avoid HIPAA Headaches
Get a free electronic and paper copy (U.S. only) of How to Avoid HIPAA Headaches, an Amazon Number One Best-Seller! Just Fill out the form below!
CONTACT
Phone: 888-997-3635
Fax:888-667-7849
Semel Consulting, LLC
6547 Midnight Pass Road #90
Sarasota, Florida
34242
COMPANY
LEGAL
FOLLOW US


© 2026 Semel Consulting, LLC